

Key Features
- Role-based: Policies are bound to roles, not individual users
- Hierarchical: Support for project-scoped resources (e.g.,
project:<id>:dataset:*) - Explicit deny: Deny statements override allow statements
- Extra constraints: Resource-specific restrictions (row-level security, column filtering, path prefixes)
- Wildcard support: Use
*for flexible matching across resources and actions - Filtered lists: Lists only return the entities you can read (
<resource>:read), so a role or scoped API key withoutpipeline:readsees no pipelines - Branch-aware: Optional branch specification for version control

Policy Structure
A policy is a list of statements that define access rules:Fields
Resource Patterns
Resources follow a hierarchical pattern that supports various levels of specificity:Flat Resources
Hierarchical Resources
Hierarchical patterns enable project-scoped permissions:Supported Resource Types
dataset- Data tables in the lakehouseproject- Project containersview- Virtual views over datasetsschedule- Automated execution schedulesextract- Data ingestion jobscompute- Compute resourcesapi_key- API authentication keysuser- User accountsrole- User rolesnotebook- Interactive analysis notebookspipeline- Data transformation pipelinesendpoint- REST API endpointsintelligent_app- Dashboard applicationsvariable- Environment variablesagent- AI agentsaction- Executable actionsorganisation- Organisation-level administrationorion- Orion logsconsole- The developer console (console:readshows it)source- Data source connectionsnotification- Notification channels and settingstag- Resource tagsruleset- Data Quality rulesetsrule_template- Data Quality Rule Library templates
Actions
Actions follow the<resource>:<action> format and define what operations can be performed:
Action Patterns
dataset:read- Read access to datasetsdataset:write- Modify datasetsdataset:delete- Delete datasetsdataset:execute- Execute operations on datasetsdataset:manage- Full management accessdataset:create- Create new datasetsdataset:*- All dataset actions*:read- Read access to all resources*:*- All actions on all resources
Common Actions
Exceptional Actions
Some resources support custom actions beyond the standard CRUD operations:project:read_repository- Read access to project code repositoryproject:write_repository- Write access to project code repository (push commits, merge pull requests)project:pr_create- Permission to open a pull request targeting a branchproject:deploy- Permission to deploy a projectendpoint:invoke- Permission to call an API endpointagent:ask- Permission to ask (query) an AI agent
Developer Console
The developer console is shown only to users withconsole:read. Every built-in role has it. To hide the console, use a role whose policies do not grant console:read, or deny it:
Manage Permissions and Settings Access
Some parts of the application — mainly the Settings area — are gated by themanage action rather than by read. A user who holds <resource>:manage sees that resource’s menu in Settings and can view its entries.
manage grants visibility only. It does not imply creating, editing, or deleting — grant <resource>:create, <resource>:write, or <resource>:delete alongside it for those operations.
Previously these areas were visible only to users with organisation:manage. Now each resource can be delegated independently, so you can grant access to a single Settings menu without handing over organisation-wide administration.
Resources that support manage
Example: access to API keys and sources
This policy reveals the API Keys and Source menus in Settings without granting any other organisation administration:api_key:manage is enough to create and revoke their own keys. Sources are shared organisation resources, so this policy does not let them create or delete a source.
Example: adding source create permission
To let the same role also create sources, addsource:create on the resource type:
source:delete and source:write on the instances (for example source:*).
organisation:manage still implies access to every Settings menu. Use the per-resource manage actions when you want to delegate one area only.Row-Level and Column-Level Security
Datazone supports fine-grained data access control through row-level and column-level restrictions using theextra_constraints field. This enables you to restrict what data users can see within a dataset or view, beyond just granting or denying access to the entire resource.
Restrictions are enforced by ClickHouse: Datazone turns them into ClickHouse row policies and column grants for each role, so they apply to every query a user runs, whether from the SQL explorer, the API or anywhere else that queries data as that user. They are synced in the background and take effect within about a minute of saving the policy.
Extra Constraints Structure
For datasets and views, you can specify columnar constraints:Fields
What the restrictions do depends on the statement’s
effect:
A
deny statement with restrictions only takes away part of the data. The dataset or view itself stays accessible: it is still listed and can still be queried. A deny without restrictions removes access to the whole resource, as usual.Row-Level Restrictions
Row-level restrictions apply SQL conditions to filter which rows a user can access:country = 'USA' AND department = 'Sales', as if every query on this dataset carried that filter.
To hide some rows and keep the rest, use deny. Combined with a broad allow, this gives access to everything except the matching rows:
- Several
allowstatements on the same dataset: a row is visible if it matches any of them. denystatements always apply on top: a row matching a deny is hidden even if an allow matches it.- NULL values: a
denyonly hides rows where the condition is true. Rows where it evaluates toNULL(for examplecityisNULL) stay visible.
Column-Level Restrictions
Withallow, only the listed columns are readable:
deny, the listed columns are hidden and everything else stays readable. For example, read access to all datasets except one sensitive column:
- An
allowlisting columns limits the dataset to those columns, even if the same role also has broader access to it (for example throughdataset:*). - When both an
allowand adenylist columns of the same dataset, the readable columns are the allowed ones minus the denied ones. - Columns added to the dataset later are hidden under an
allowlist and visible under adenylist. Prefer anallowlist for sensitive data.
Querying a dataset with hidden columns
Hidden columns are not silently dropped from results. ClickHouse rejects any query that reads a hidden column, includingSELECT * and filters such as WHERE password = ...:
Combined Restrictions
You can use both row and column restrictions together:Users with Several Roles
Row and column restrictions are combined differently when a user has more than one role:- Column restrictions are applied per role, and roles add up: if any of the user’s roles can read a column, the user can read it. A column hidden in one role is still readable if another role grants the whole dataset.
- Row restrictions apply to the user directly, whichever role they come from: a row restriction in one role narrows the rows the user sees even if another role grants the whole dataset.
Limitations
- Restrictions follow column names, not columns. If a column is renamed (for example
passwordtopwd), a restriction on the old name no longer applies to it. Review the policies of a dataset after renaming its columns. - Row conditions are checked by ClickHouse at query time. A condition that refers to a column the dataset does not have makes every query on that dataset fail for the affected users, until the condition is fixed.
- Views are restricted separately. A view reads its source with its own permissions, so restrictions on a dataset do not carry over to views built on it. Add the same restrictions to the view.
- Only queries through ClickHouse are covered. Restrictions are enforced by the database, not by the files underneath it.
Policy Examples
Read-Only Access
Grant read access to all resources:Dataset Admin
Full control over all datasets:Project Admin
Full control over a specific project and all its resources:- Manage the project itself (
project:*) - Create and manage all child resources (datasets, notebooks, pipelines, etc.)
Restricted Access with Deny
Allow read access to all datasets except one specific dataset:Project-Scoped Dataset Access
Grant access to datasets within a specific project only:Branch Protection
Repository permissions can be scoped to a branch with thebranch field. Combined with the separation between project:write_repository (pushing commits and merging pull requests) and project:pr_create (opening a pull request), this lets you protect a branch such as main while keeping the rest of the project fully editable.
The result is a familiar protected-branch workflow: contributors work on feature branches and open pull requests into
main, but nobody with this policy can push or merge into main directly. Grant merge rights to a separate reviewer role that is not denied project:write_repository on main.
project:pr_create is checked against the base branch of the pull request — the branch being merged into. To block pull requests into main entirely, add project:pr_create to the deny statement’s actions.Data Analyst Role
Typical permissions for a data analyst:Built-in Policies
Datazone provides several built-in policies for common use cases:Admin Policy
Full access to all resources:Access Map
The Access Map shows who can do what as a graph: users on the left, the roles they hold in the middle, and the policies those roles grant on the right. Open it from Settings → Users → Map, or click Open in access map on any user, role or policy page.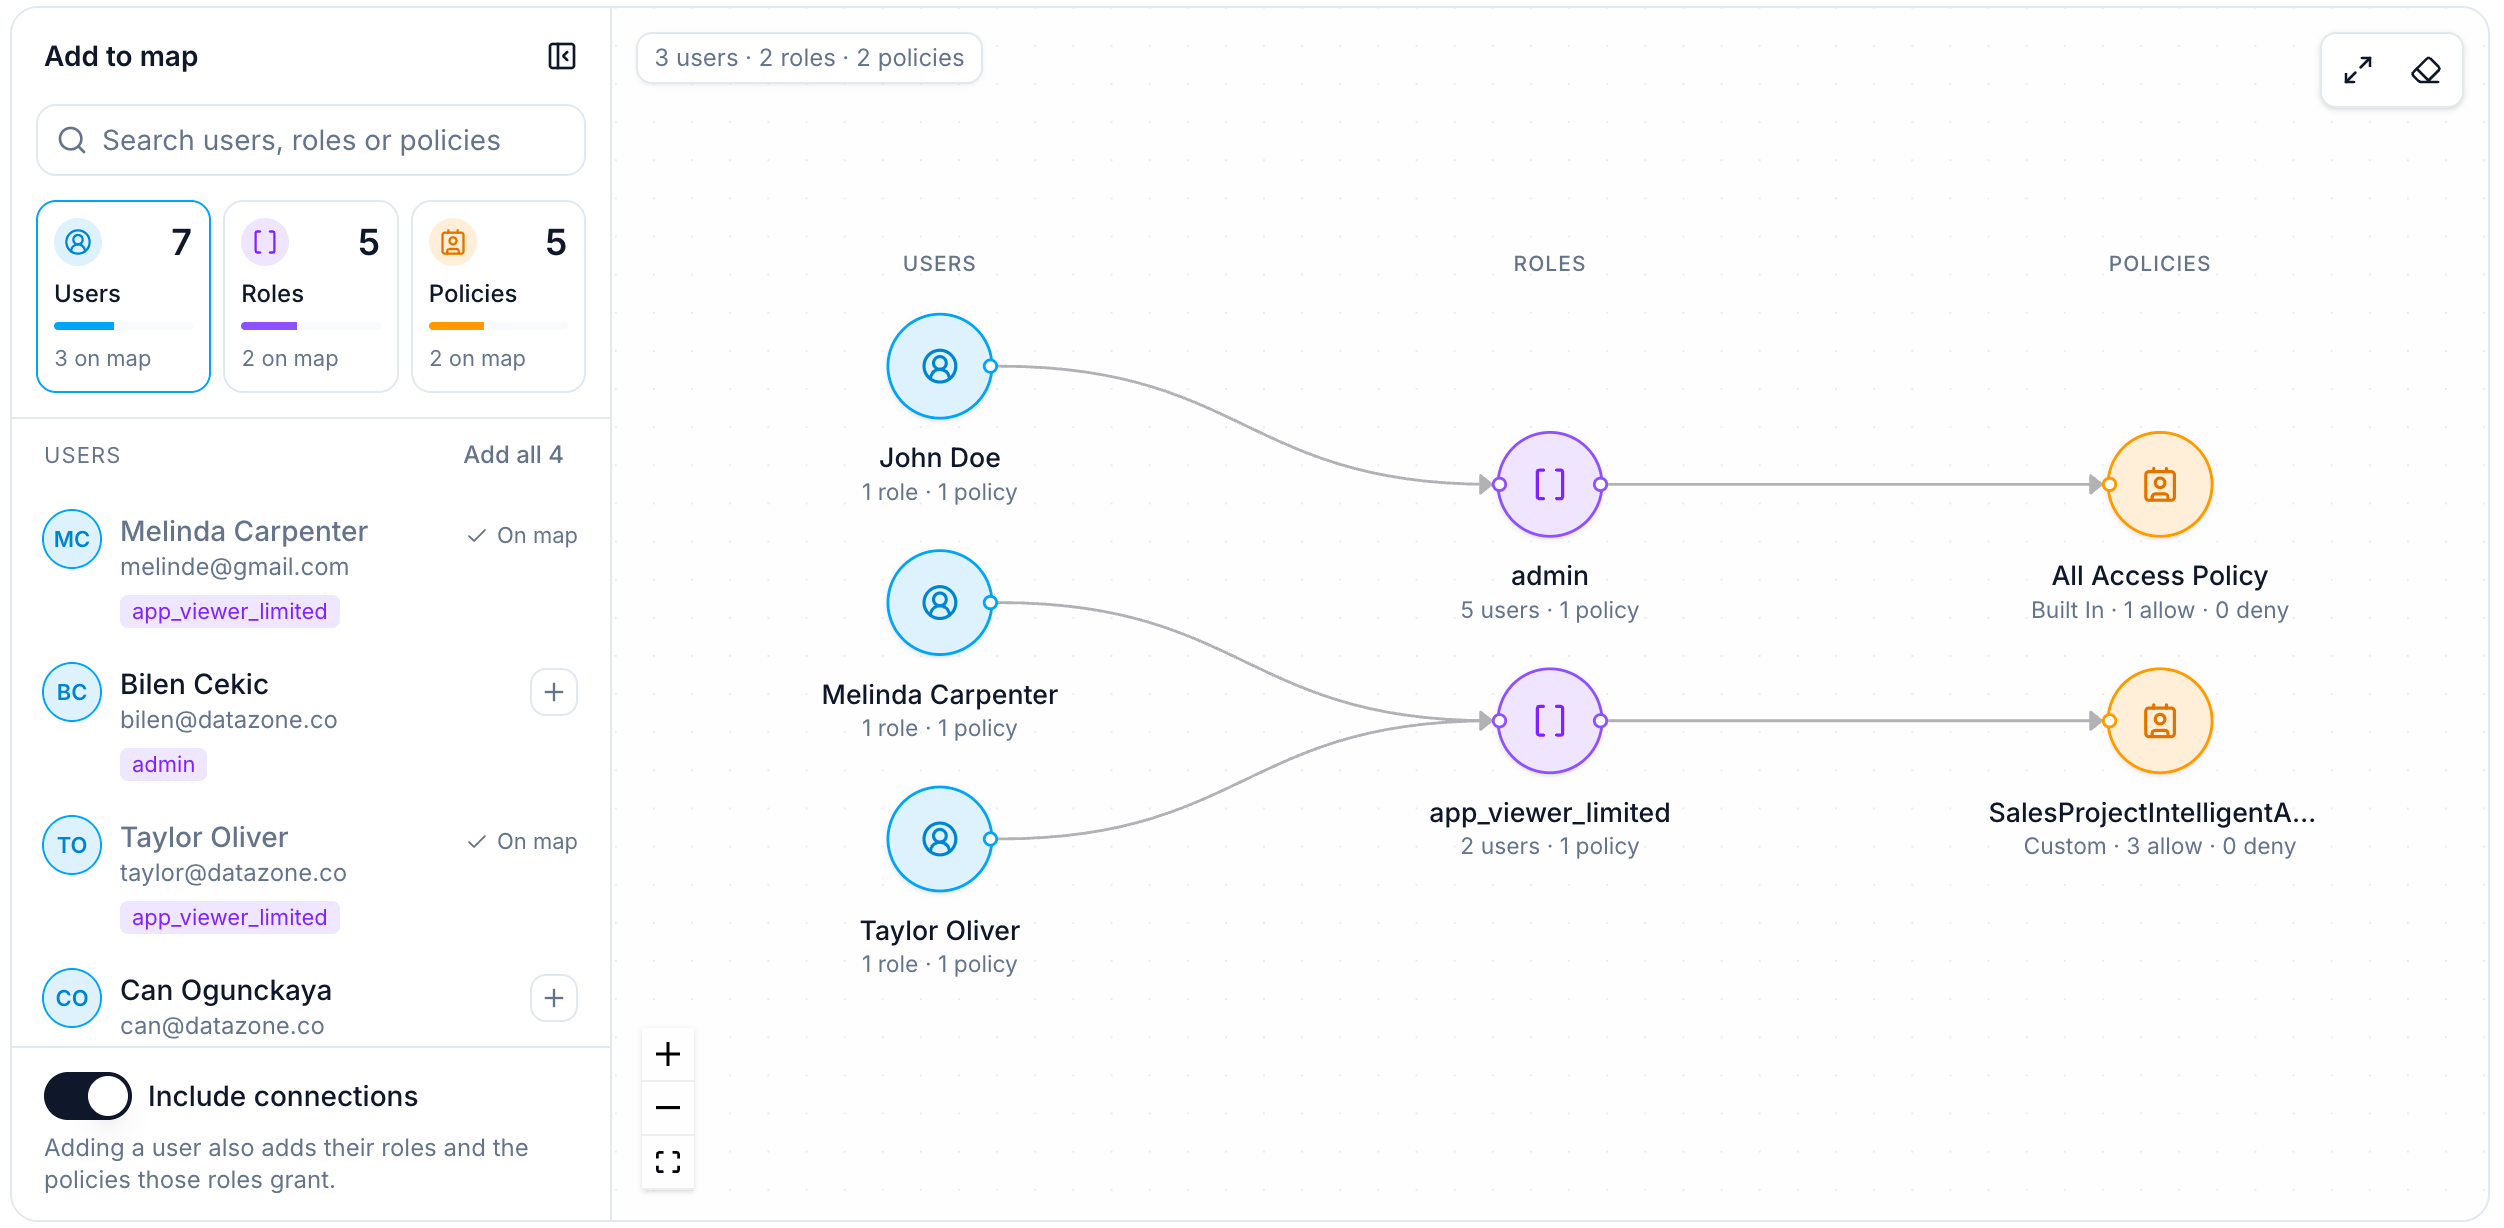
- Add to map: search users, roles or policies in the side panel, then click one or drag it onto the canvas.
- Include connections: when on, adding a user also adds their roles and the policies those roles grant; adding a role adds its policies; adding a policy adds the roles that use it.
- Inspect: click a node to see its connections, effective policies, and each statement’s resources, actions, row filters and restricted columns.
- Add several users side by side to compare their access, and use Full screen or Clear map from the toolbar.
Best Practices
Policy Design
- Start restrictive: Begin with minimal permissions and add as needed
- Use hierarchical patterns: Organize permissions by project for better management
- Leverage deny sparingly: Use deny for exceptions to broad allow rules
- Document policies: Add clear descriptions to explain policy intent
Role Assignment
- Bind to roles only: Policies are assigned to roles, not individual users
- Create role hierarchies: Use multiple roles for different permission levels (Viewer, Editor, Admin)
- Audit regularly: Review policy assignments periodically
Performance
- Cache aware: Policies are cached; changes may take a few seconds to propagate
- Granular resources: Use specific resource IDs when possible to reduce evaluation complexity
- Minimize deny statements: They require checking all policies
Security
- Principle of least privilege: Grant only necessary permissions
- Explicit denies: Use deny statements to override broad allows for sensitive resources
- Extra constraints: Apply row-level and column-level security for sensitive data
- Path restrictions: Use
path_prefixconstraints to sandbox project access
Validation Rules
Policies are validated automatically to ensure correctness:Action Format
- Must follow
<resource>:<action>pattern - Both parts must be lowercase with underscores
- Wildcards allowed:
*:*,dataset:*,*:read
dataset:readproject:**:*
dataset(missing action)Dataset:Read(uppercase)read(missing resource)
Resource Pattern
- Must be valid resource type or wildcard
- ObjectIds must be valid MongoDB ObjectIds
- Hierarchical patterns must follow
parent:<id>:childformat
dataset:*project:507f1f77bcf86cd799439011project:507f1f77bcf86cd799439011:dataset:*
dataset:invalid-idproject::dataset:*
Action-Resource Matching
Actions must match the resource type they’re applied to:*:*) can be used on any resource.
Troubleshooting
Permission Denied Errors
If you encounter permission denied errors:- Check user roles: Verify the user has the appropriate role assigned
- Review policy statements: Ensure the policy includes the required action and resource
- Look for deny statements: Check if an explicit deny is overriding an allow
- Verify resource IDs: Ensure you’re using the correct resource identifier
- Check cache: Wait a few seconds for policy changes to propagate
”Not enough privileges” on a Dataset You Can Read
If a query fails withNot enough privileges on a dataset the user can otherwise read, a column restriction hides one of the columns the query uses:
- Avoid
SELECT *: List the columns explicitly, or exclude the hidden ones withSELECT * EXCEPT (column) - Check filters and joins: Using a hidden column in
WHERE,JOINorGROUP BYalso needs access to it - Review the policy: Look for
column_level_restrictionson the dataset in the user’s roles
Hierarchical Permissions Not Working
If project-scoped permissions aren’t working:- Verify pattern format: Use
project:<id>:*notproject:*:<id> - Check parent context: Ensure the resource creation includes project reference
- Review cache: Hierarchical relationships are cached; wait 5 minutes or invalidate cache
- Validate ObjectIds: All IDs must be valid MongoDB ObjectIds
Performance Issues
If policy evaluation is slow:- Reduce policy complexity: Simplify nested hierarchies
- Use specific resources: Prefer
dataset:<id>over broad wildcards when possible - Monitor cache health: Ensure Redis is functioning properly
- Check database queries: Hierarchical policies should use cache, not database
Related Resources
Roles
Learn about role management and user assignment
Authentication
Understand authentication and token management
API Keys
Generate and manage API keys for programmatic access
Projects
Organize resources within projects